Cache: reuse a response without losing freshness or privacy
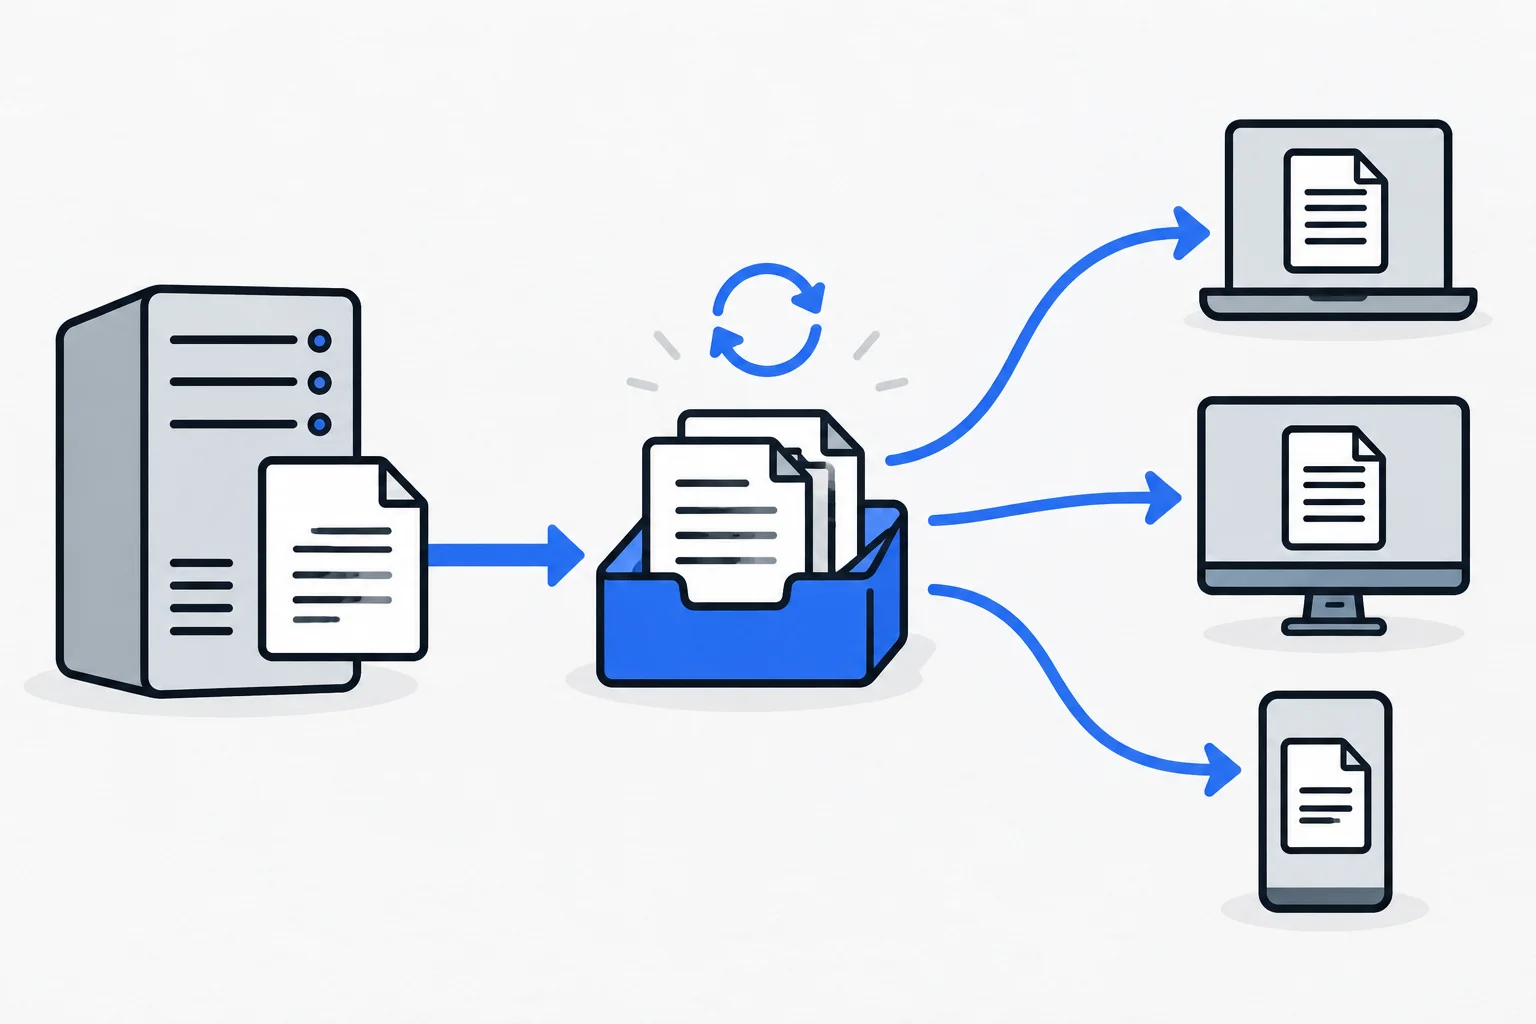
A cache stores a previously prepared response or resource for reuse under suitable conditions. On the web, it can exist in the browser, an intermediary network layer or the server. Its purpose is to reduce unnecessary transfer and processing while preserving freshness and appropriate access.
Also known as: cache · HTTP cache · page cache
At a glance
- A cache reuses a copy; it is different from a search index.
- Public and personalized responses need different storage rules.
- A faster stored response is useful only while it remains correct and appropriate to serve.
On this page
Why reuse an earlier response?
Regenerating the same article illustration for every visitor can be unnecessary. When the file has not changed, a stored copy can arrive with less serving work. A browser may even avoid another complete download.
MDN's caching guide explains reuse under rules defining which response can be stored, for how long and under which conditions.
A search engine's index is different from the cache delivering the website to visitors.
Which types of cache exist?
A browser's private cache belongs to that client. A shared cache can serve several visitors, while an application can internally store query results or generated pages.
A CDN is a distributed delivery network that often uses caching, not another name for the cache itself. Placement affects who can receive a stored response and which processing can be avoided.
A personal account page and a public definition therefore need different treatment. One can differ by user while the other may be identical for everyone.
What are freshness and revalidation?
A response can remain fresh for a defined period. Later, a cache may check whether the source changed. If unchanged, it can reuse the body without transferring it completely again.
The directive no-cache does not necessarily forbid storage; it requires validation before reuse. no-store instructs caches not to store the response. private prevents shared caching while potentially permitting browser storage.
These are caching rules, not a substitute for authorization. The application must still protect confidential content correctly.
Example: a menu and a reservation confirmation
Imagine a restaurant's public menu changing daily while reservation confirmations contain individual names and times. A short-lived shared menu response may be sensible. A guest's confirmation must not be served to another guest from a shared copy.
If a menu price changes, plan how stored copies update. The editor's saved value and the version delivered publicly can temporarily differ.
This fictional example makes correctness and speed joint requirements. The fastest response is still wrong if it exposes another guest's information or an obsolete price.
How should behavior be checked?
Test first and repeated requests, anonymous and signed-in states, and requests after an update. HTTP statuses and headers help explain behavior, but inspect the actual content too.
Changes in TTFB can indicate faster serving when measured under comparable conditions. Cold and warm caches can produce different legitimate experiences.
What does this mean for publishing?
After an edit, verify the public page instead of only the editor. This matters particularly for prices, availability and corrections.
Caching is one tool within reliable technical SEO. It does not guarantee rankings or replace content maintenance. It succeeds when the appropriate reader receives valid information with less unnecessary waiting.