Prompt injection: meaning, examples and practical use
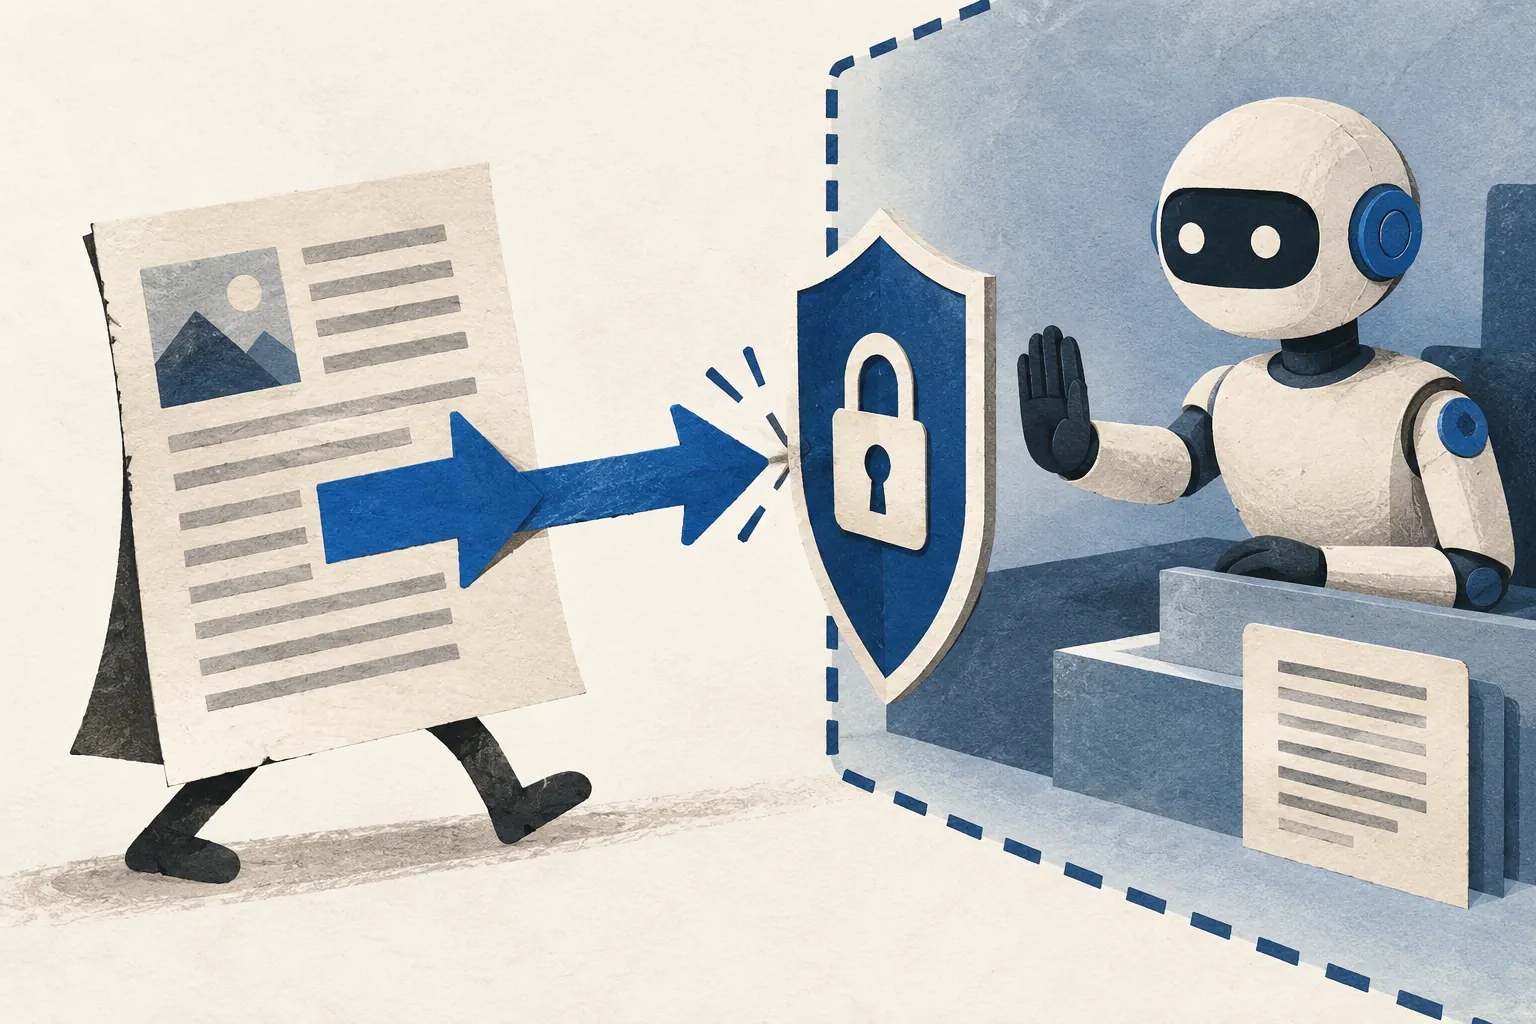
Prompt injection is an attempt to redirect an AI system from its authorized task using instructions placed in content it processes. In an indirect injection, those instructions may appear in a web page, document or email. Reading an outside source does not turn that source into an authorized user instruction.
Also known as: indirect prompt injection
At a glance
- External content can inform a task without gaining authority over it.
- The impact can increase when the system can send data or perform actions.
- One warning sentence or filter does not establish complete protection.
On this page
How it differs from a normal request
A user asks for a task, such as summarizing a guide. Text inside that guide may then try to change the task. The central problem is confusing material being processed with instructions authorized to control the system.
Anthropic’s browser-use research describes this risk in outside pages and other retrieved material, while emphasizing that defenses remain an active research problem. Research overview
Example: replacing a comparison with promotion
Imagine an assistant comparing two product manuals. One page contains text attempting to make it abandon the comparison and repeat a particular offer.
That text is not the user’s request. It is, at most, part of the material being examined. Treating it as a command would cross the authority boundary. This example illustrates the distinction rather than providing an attack procedure.
An evaluator can check whether the final output still addresses the comparison and whether any change in behavior was actually authorized by the user.
Why tools change the consequences
A text-only summarizer may produce a misleading response. A system able to send messages, upload information or modify settings can expose additional actions to the same attempted redirection.
Give tools only the access necessary for the task and connect sensitive actions to genuine user intent. RAG does not automatically make every retrieved document trustworthy.
Sources provide evidence, not authority
An AI citation can identify where a claim came from without authorizing that source to control the system. Embedded requests, role claims and apparent system messages still need to be treated according to their origin.
Defenses can combine separation of data and instructions, restricted permissions, action checks and targeted evaluation. A prohibitive sentence in a prompt alone cannot establish complete security. During editorial review, retain the original task and assess what the source actually supports.