What is HTTPS?
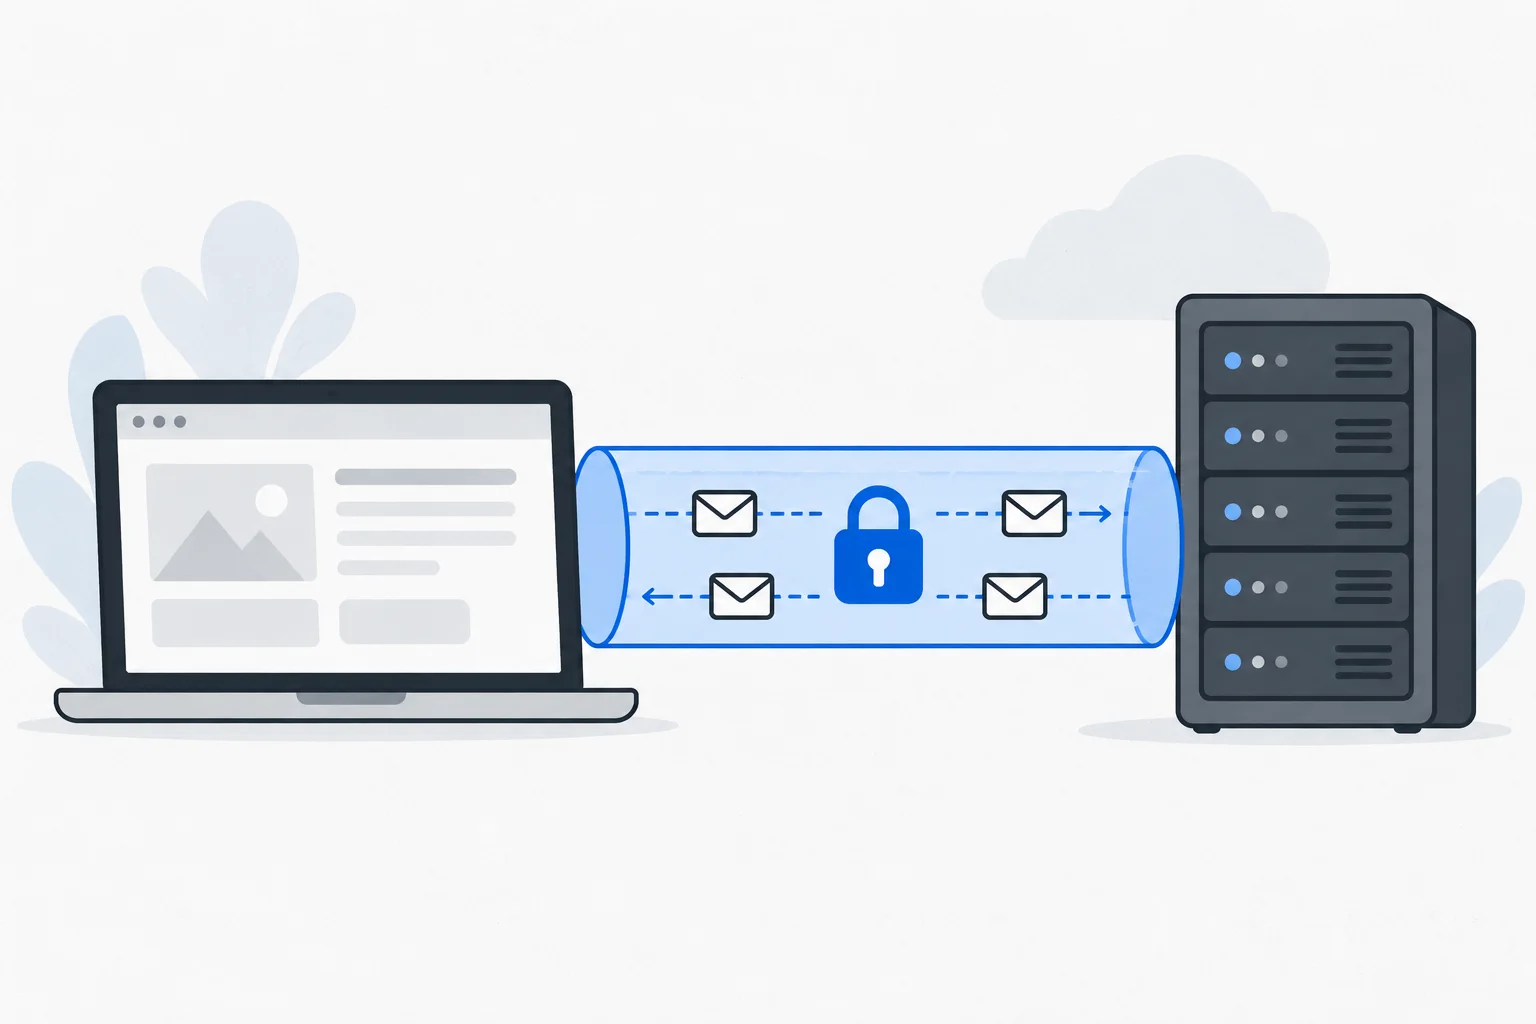
HTTPS is HTTP protected by TLS, which encrypts data in transit, helps prevent modification of that data and authenticates the server involved in the connection.
Also known as: secure HTTP · encrypted web connection
At a glance
- HTTPS protects the connection; it does not certify that a business or article is trustworthy.
- HTTP and HTTPS are distinct URL versions that need consistent handling.
- Certificates, redirects and loaded resources all affect a successful migration.
On this page
What does the encrypted connection protect?
Data travels between a visitor’s browser and the server when a page loads or a form is submitted. HTTPS uses TLS to protect that connection, making it harder for an intermediary to read or alter the traffic.
Several networks can sit between the visitor and the website. Transport protection matters across that path, but it does not replace access controls, secure application code or appropriate data handling. Security has several layers.
What does a certificate establish?
During connection setup, the browser checks the certificate presented by the server and whether it is valid for the connection. A problem can produce a warning.
A working HTTPS connection is therefore an important technical foundation. It is not a professional qualification, a purchase guarantee or a fact-check of the website’s articles. A malicious website can use HTTPS too.
Describe its value precisely: it protects communication when the required conditions are satisfied. Do not present it as a general seal proving that every business claim is reliable.
Why are HTTP and HTTPS different URLs?
http://example.com/guide and https://example.com/guide are separate addresses. If both independently serve the same content, the relationship between them needs to be managed.
A permanent redirect can send visitors from the old HTTP address to the corresponding HTTPS page. A canonical URL supplies a different kind of signal and does not itself move the visitor.
Update your own menus, content links and resource URLs to the chosen secure addresses as well. Otherwise, each interaction can begin with an unnecessary old address or load an insecure resource.
An example: upgrading a tutor’s website
Imagine a tutor whose old site used HTTP. After an upgrade, HTTPS works, but the contact button still points to the old address and several images use old resource URLs.
Opening the home page once does not verify the whole migration. The owner checks the home page, service details, learning articles and contact form, redirects the corresponding old URLs, updates internal links and inspects loaded resources.
If an external service stores an old callback or website address, that configuration may also need attention. A migration involves connected URLs, not just one switch.
Does HTTPS mean the page is available or indexed?
No. A secure connection can return a 404, a 500 or another error. Establishing the connection and processing the application request successfully are different steps. The HTTP status code describes the response.
A working HTTPS page can also deliberately exclude itself from indexing. Encryption does not override search instructions or other indexing requirements.
Keep certificates, important redirects and resource addresses maintained over time. Hosting automation may handle much of that work, but changes should still be checked on the actual site. HTTPS is valuable for its specific protection; it needs no promise of guaranteed rankings or business credibility to justify using it.